Appearance
For the hiring use case, imper.ai requires the following Microsoft Entra ID / Microsoft Graph permissions to schedule interview events on participants' calendars, verify that the interview session happened, and identify the interviewers involved.
This article explains which permissions are required and why they are needed. It applies to both ways of granting them - tenant-wide, or scoped to a security group. The permissions, and what imper.ai does with them, are the same either way; the routes differ only in whose calendars and meetings they cover.
How Permissions Are Granted
Permissions are granted during the Microsoft Entra consent flow when an administrator authorizes imper.ai in the Azure / Entra portal. They are approved at the tenant level.
NOTE
Some permissions require a Global Administrator or Application Administrator role.
IMPORTANT
OnlineMeetings.Read.All and OnlineMeetingArtifact.Read.All are not usable from consent alone. A Teams application access policy has to name imper.ai's application first - see Grant Access to Teams Meetings.
Permissions Requested by imper.ai
imper.ai uses these permissions to schedule interviews, verify they took place, and identify interviewers. They fall into three groups:
- Calendar -
Calendars.ReadWrite(not applicable to Greenhouse) - Directory -
User.ReadBasic.All - Teams meetings and attendance -
OnlineMeetings.Read.AllandOnlineMeetingArtifact.Read.All
Calendars.ReadWrite (Not Applicable to Greenhouse)
Type: Application
Used for:
- Reading interview invites and creating/updating the interview events on participants' calendars
OnlineMeetings.Read.All
Type: Application
Used for:
- Reading the Teams meeting the interview is held in, so imper.ai can match the meeting to the scheduled interview
OnlineMeetingArtifact.Read.All
Type: Application
Used for:
- Reading that meeting's attendance report, so imper.ai can confirm the candidate actually attended - available within minutes of the interview ending
User.ReadBasic.All
Type: Application
Used for:
- Reading basic profile information (user ID, display name, and email) to resolve interviewer identities from the tenant directory
CallRecords.Read.All (Retiring)
Type: Application
Used for:
- Reading the interview call details as a fallback source of attendance, where an attendance report is unavailable
NOTE
imper.ai will retire CallRecords.Read.All in the near future. Microsoft can take up to 5 days to publish a call record, so the meeting's attendance report (OnlineMeetingArtifact.Read.All) is now the primary source of attendance. Keep CallRecords.Read.All approved until the retirement is complete.
How These Permissions Are Used
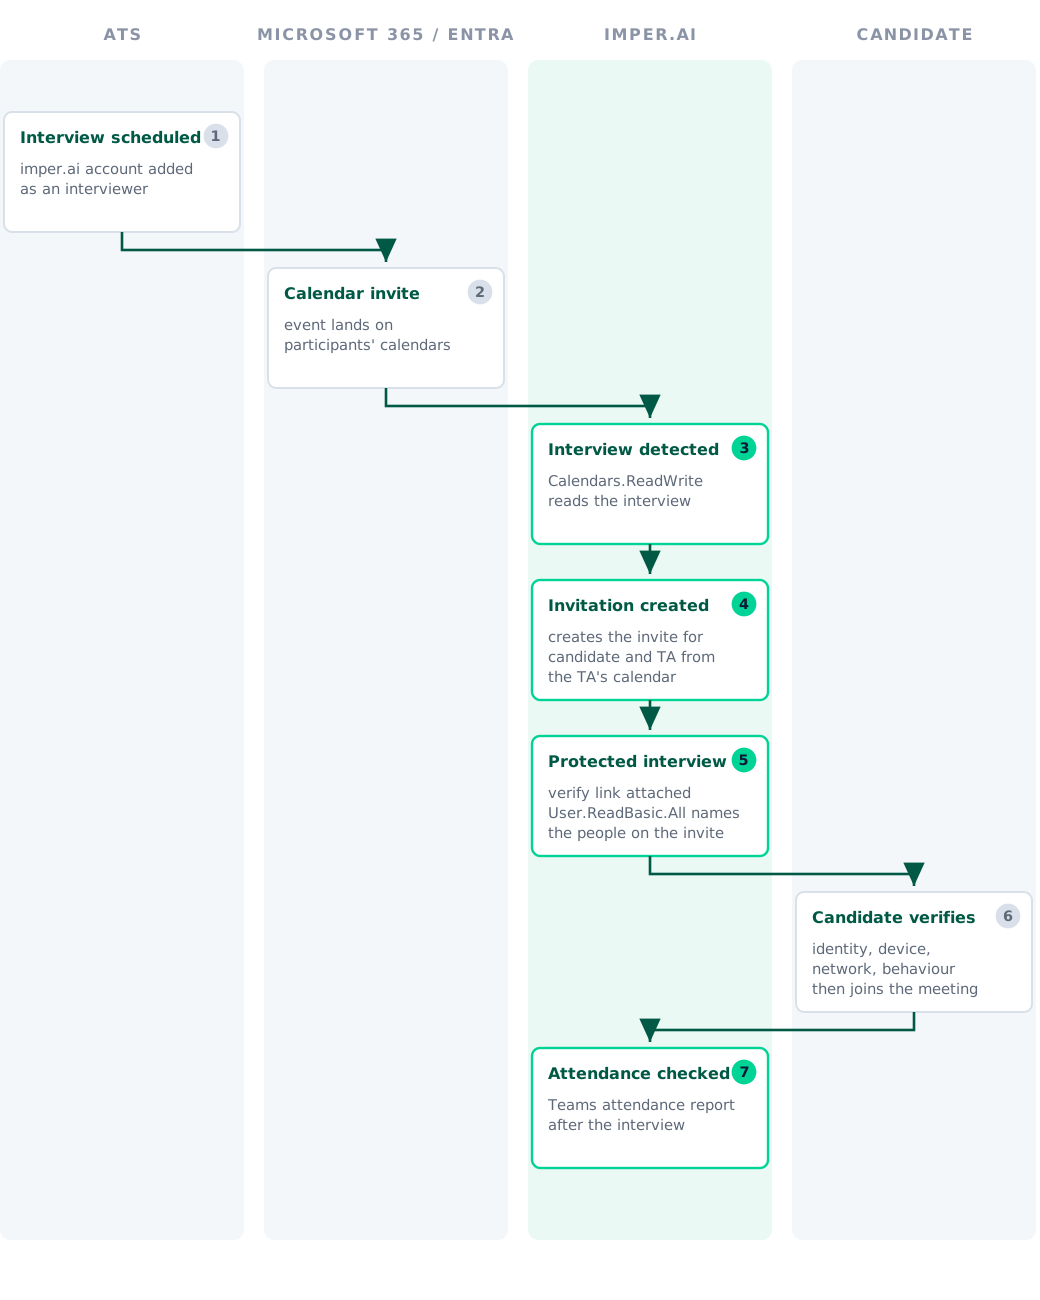
The flow below illustrates how imper.ai integrates with the existing interview workflow. When an interview is scheduled, imper.ai detects it through the connected calendar, associates it with the relevant interview, and updates the calendar event with a verification link. The candidate completes verification before joining the meeting. After the interview, imper.ai reads the meeting's attendance report to confirm that the interview took place and identify who attended, falling back to the Microsoft Teams call record where no report is available.
How imper.ai Connects to Microsoft 365
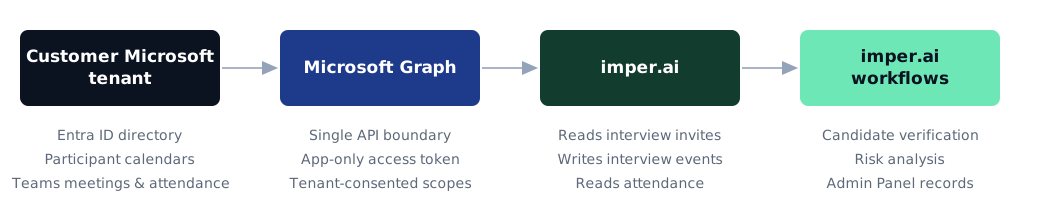
imper.ai connects to Microsoft Graph using the application identity created when you connect your Entra tenant. Access is governed entirely by the permissions your administrator approves during consent.
Application Access, Not Delegated Access
All permissions above are Application type. imper.ai authenticates to Microsoft Graph as an application - it does not require a signed-in user and does not impersonate an individual employee.
Microsoft Graph access is limited to the permissions listed on this page. Candidate verification, risk analysis, and device/network signal collection are performed by imper.ai directly and do not require Microsoft Graph access.
Access Scope and Controls
By default, Application permissions are granted at the tenant level. OnlineMeetings.Read.All and OnlineMeetingArtifact.Read.All are the exception: consent alone grants them no meeting at all, and the Teams application access policy that names imper.ai's application is what decides whose meetings it can read.
Where more restrictive access is required, you can limit imper.ai's access to only the users involved in the Hiring workflow - see Scoping Microsoft 365 Access to a Security Group for implementation details.